Update at a glance
- Incident: Alleged Westco Motors Cairns data exposure
- Reporting status: Unverified threat-actor claim
- Australian relevance: Cairns, Queensland; automotive customer data
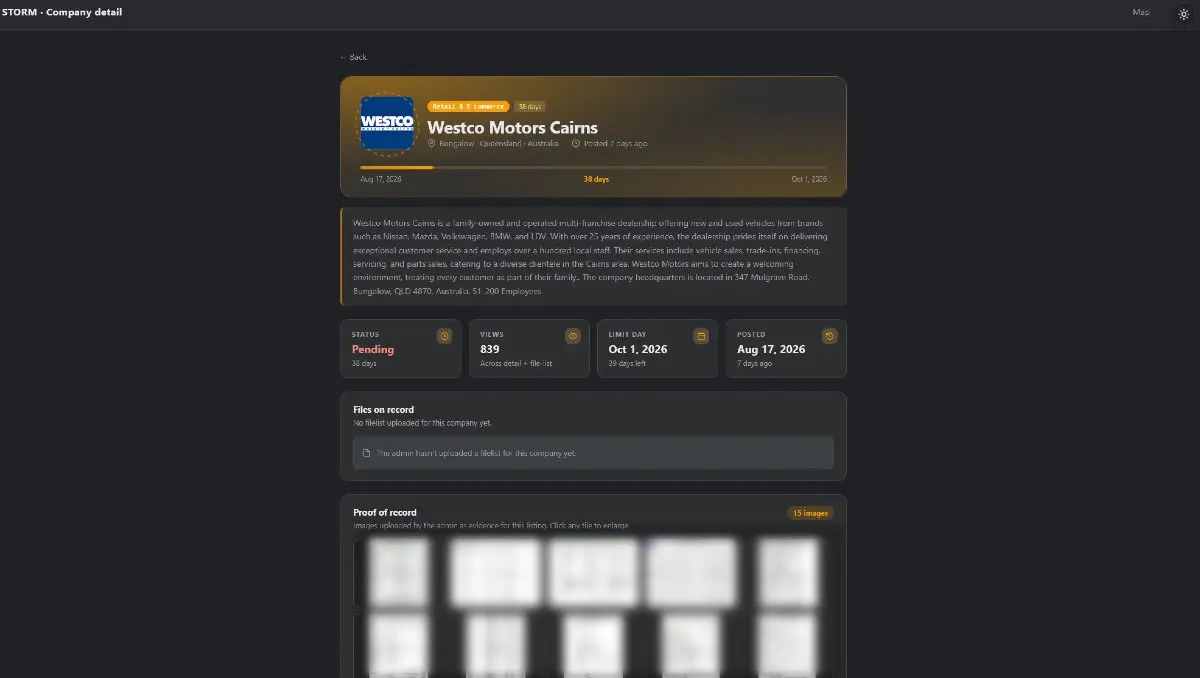
The Storm group has published files it claims belong to Westco Motors Cairns. The allegation has not been independently confirmed, but organisations holding customer financial or contact records should use the report as a prompt to verify exposure, preserve logs and confirm recovery readiness.
By Compuloop
Storm ransomware Westco Motors Cairns: Breaking update at a glance
- Storm ransomware group posted documents it claims are from Westco Motors Cairns on a darknet leak site.
- Published items reportedly include vehicle identification numbers (VINs), tax invoices and customer contact details.
- The threat actor claims it intends to release additional material on 12 October. The volume and authenticity of any further release remain unverified.
What has been reported
Unverified claims
- There is no independently published confirmation from Westco Motors Cairns or from an official regulator (OAIC or state authority) in publicly available information that the business has acknowledged compromise.
- The threat actor claims it will publish additional data on 12 October, but the size, authenticity and scope of any further release remain unconfirmed.
- No verified ransom amount, initial access method or evidence of successful encryption was publicly available at publication.
What remains unknown
- Whether Westco Motors Cairns experienced an extortion-driven ransomware encrypt-and-demand event, or whether this is a data-theft-only incident staged to pressure the organisation.
- The total volume of data allegedly held by the threat actor and whether backups were affected.
- Any impact on customers, partners or suppliers; notification or regulatory action status is not publicly reported at this time.
Practical actions (immediate checklist)
- Verify: Ask your IT provider to search for indicators of compromise — unusual admin logins, unexpected RDP/remote-access sessions and recent data exfiltration tools. Preserve logs for forensic review.
- Contain: If intrusion is suspected, isolate affected endpoints and restrict remote-access protocols pending investigation.
- Protect customer data: If you hold similar records (VINs, invoices, contact numbers), pre-notify legal and privacy leads and prepare an incident register to meet potential OAIC reporting thresholds.
- Confirm backups: Validate offline and immutable backups, and rehearse recovery on a segmented test environment before any restore.
- Communicate: Draft factual, measured messaging for customers and staff; avoid speculative details until forensics confirm the scope.
How Australian organisations can verify exposure
Start with internal searches for files matching names, invoice patterns or VIN formats shown in the leaked samples. Use endpoint detection tools to hunt for data-compression utilities, scheduled exfiltration scripts or unusual archive files created around the reported timeframe. If you cannot confidently assess exposure, retain a reputable incident responder to preserve evidence and rule out lateral movement.
When to involve regulators or law enforcement
If personal information was accessed and there is a reasonable likelihood of harm, the Privacy Act’s mandatory breach notification rules may apply; consider early engagement with the Office of the Australian Information Commissioner (OAIC) and your local police cyber unit. For clarity on thresholds, legal counsel or a privacy specialist can advise on required notifications.
What Australian businesses should learn from this report
Ransomware actors increasingly combine data theft with public shaming to increase pressure. Even small dataset leaks — customer contact lists and invoices — can produce phishing cascades and impersonation attacks that affect suppliers and customers. Organisations in retail, automotive services and small-to-medium professional services should treat customer contact data as high-risk and protect it accordingly.
Essential Eight and control lessons
| Priority | Action |
|---|---|
| Application control | Implement allowlisting for business-critical servers to prevent unauthorised binaries. |
| Backups | Maintain offline, immutable backups and test restores regularly. |
| Multi-factor authentication | Enforce MFA on all remote access and administrator accounts. |
| Patching | Prioritise patching internet-facing services and known exploited CVEs. |
FAQ
Q: Does this report prove Westco Motors Cairns was breached?
A: No. A threat actor has posted files it attributes to Westco Motors Cairns, but neither the dealership nor an Australian regulator had publicly confirmed a breach at publication.
Q: How can I check if my organisation’s data appears in a leak?
A: Search public leak sites and paste-scan services for company names, customer email domains and sample invoice formats. Do not provide credentials to unknown services. Engage a forensic team for thorough review.
Q: Is immediate payment ever advisable?
A: We do not recommend paying without expert advice; payment does not guarantee deletion or non-disclosure. Prioritise containment, forensic analysis and regulator notification as required.
Related Compuloop guidance
- Compuloop — Cyber security services — for response engagement and incident readiness.