Devices and paths
Firewalls, VPNs, switches, wireless access and the trust paths between internal, remote and cloud services.
Choose a broad network assessment or a focused server review. Both produce reviewed evidence, prioritised findings and one defined recheck—not a raw scan export.
A firewall, switch, server, wireless network, cloud tenant and backup platform each answer a different security question. The assessment starts by defining which of those components are reachable and authorised for review.
That scope matters: an offline device, unsupported operating system, inaccessible management interface or third-party platform cannot be treated as if it was assessed. Limitations are recorded beside the findings.
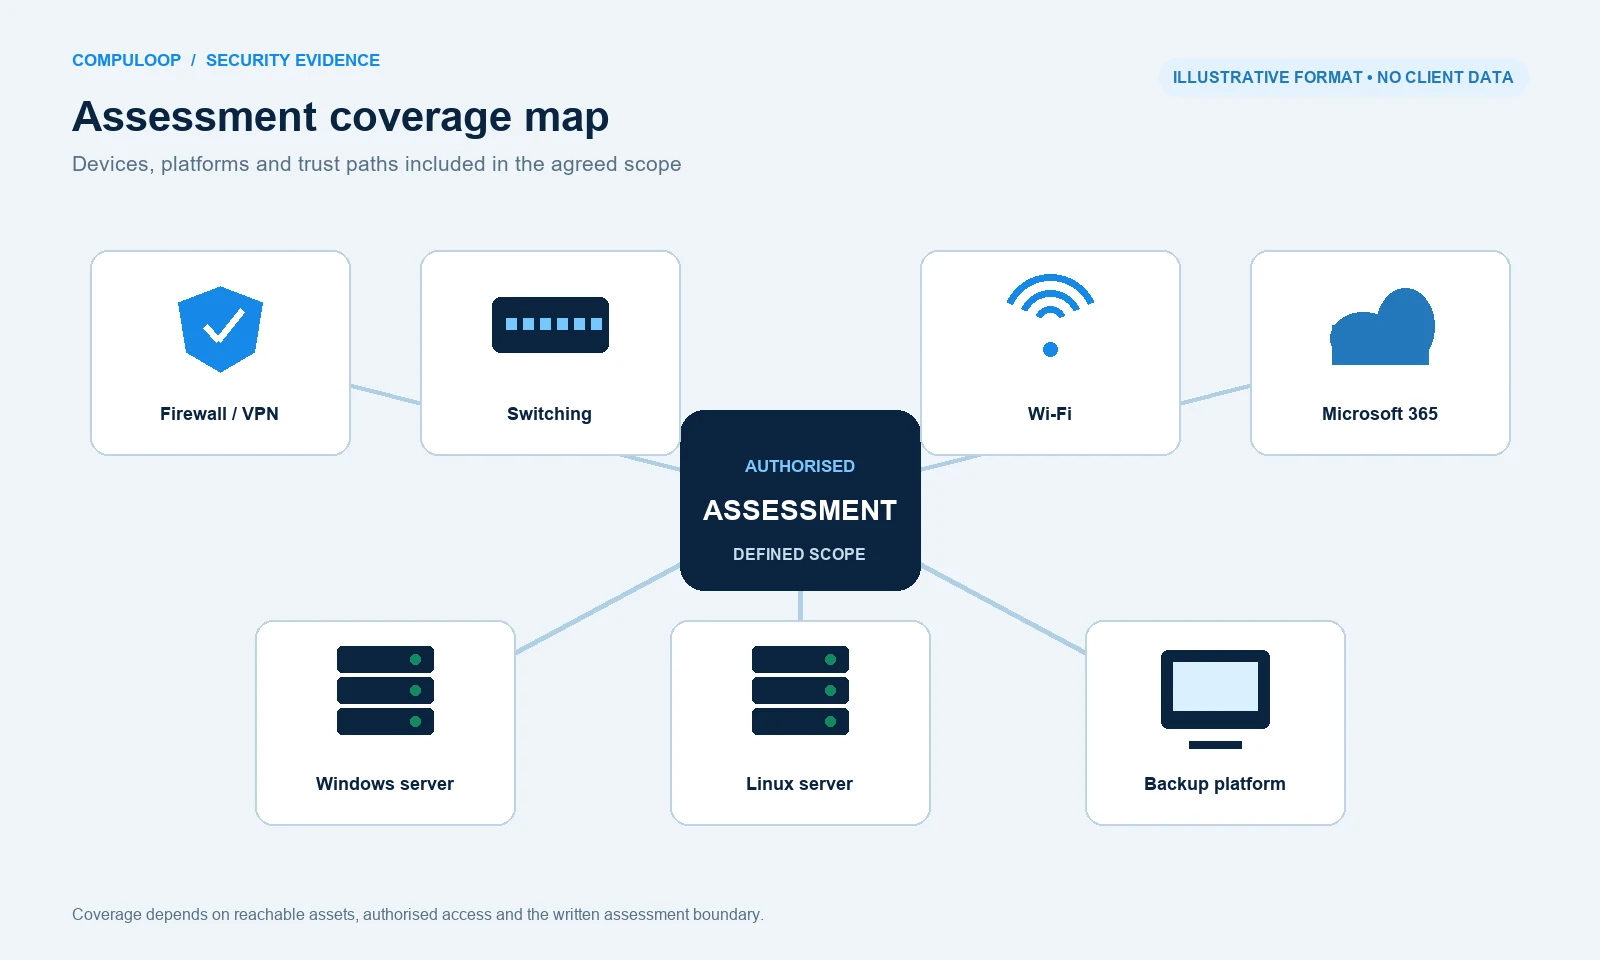
Firewalls, VPNs, switches, wireless access and the trust paths between internal, remote and cloud services.
Supported Windows or Linux servers, exposed services, privileged access, Microsoft 365 touchpoints and agreed management platforms.
Backup administration, isolation assumptions and the systems that must be available for an effective recovery.
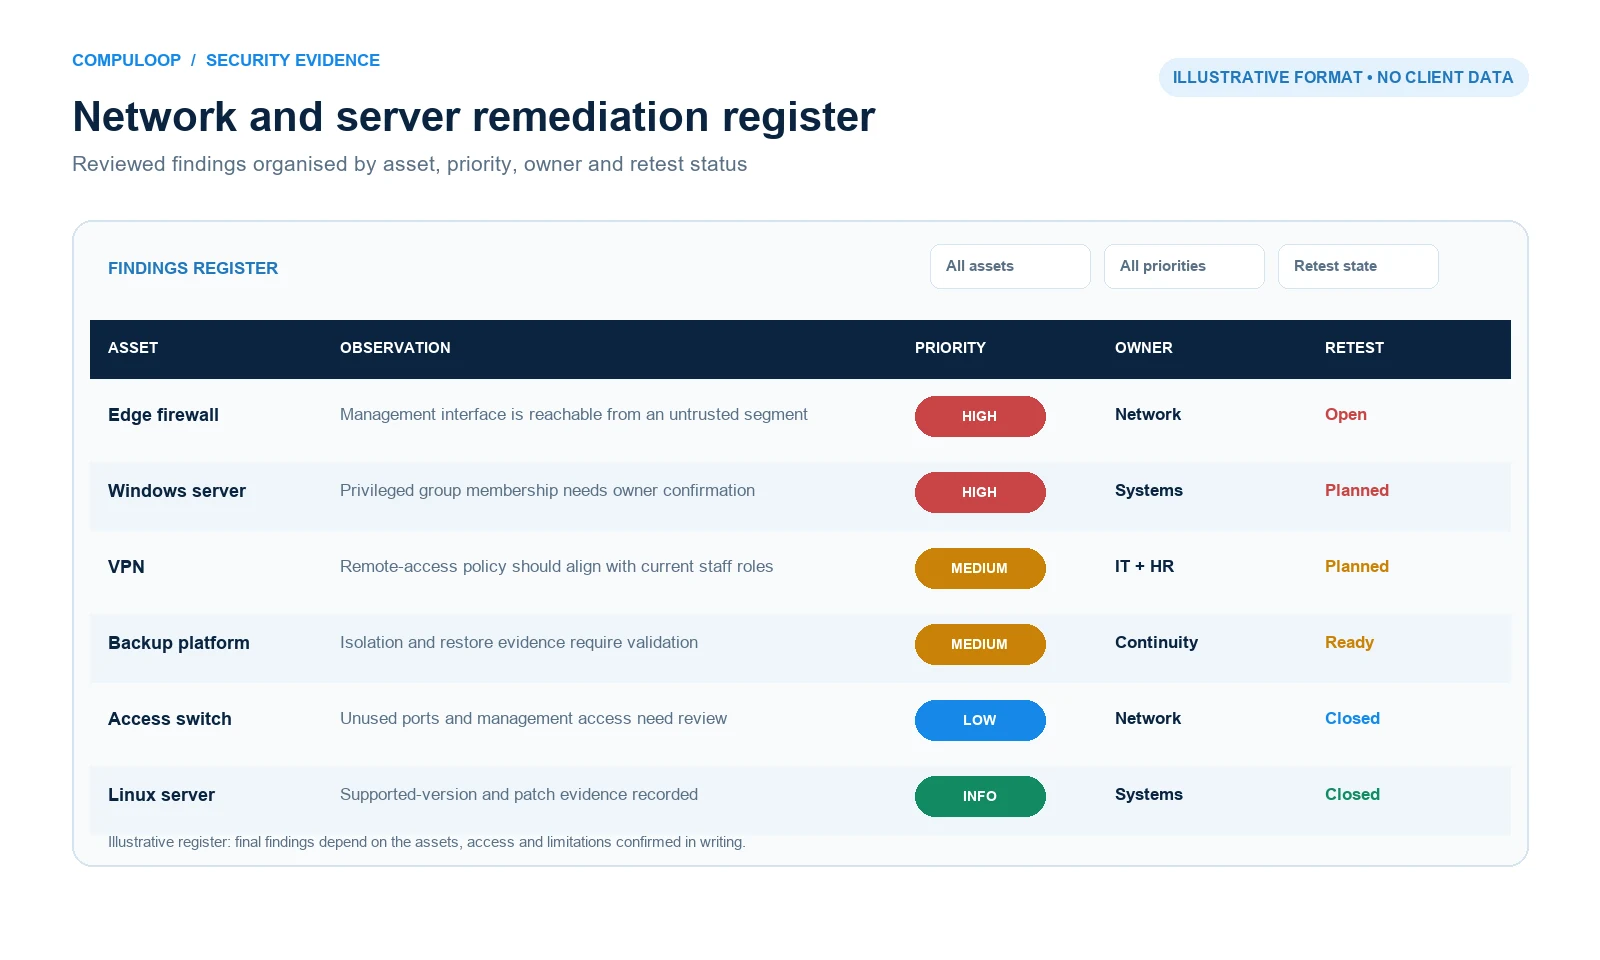
Compuloop can supply and manage security and monitoring applications after the assessment identifies the real gap. That keeps the recommendation tied to an asset, owner and operational outcome—not a random licence list.
 Discover and observe
Network discovery, topology and monitoring can make device relationships and changes easier to see after the assessment.
Ask about Auvik Secure access and traffic
Firewall, SASE and zero-trust access options can strengthen internet, branch, remote-user and application pathways.
Ask about Check Point Coordinate controls
Firewall, endpoint, server and managed detection options can be aligned through the Sophos security stack where appropriate.
Ask about Sophos Detect and respond
Endpoint, server, cloud and identity protection options can support detection, investigation and response after gaps are prioritised.
Ask about SentinelOne Protect and recover
Vulnerability assessment, endpoint protection, backup and recovery can be combined when resilience and remediation need one managed path.
Ask about Acronis Secure Microsoft environments
Defender, Entra and related Microsoft security capabilities can be scoped against existing licences, identities, devices and workloads.
Ask about Microsoft SecurityHow this works: these are optional technology choices—not products automatically included in every service. Compuloop confirms the operational need, licence eligibility, Australian availability, data region, compatibility and final commercial scope before supply.
Use the network route for one business site with multiple reachable assets. Use the server route when a specific Windows or Linux workload needs closer attention.
One site or network, up to 25 reachable assets.
Working remote access is required. Offline assets and remediation are excluded.
One supported Windows or Linux server.
Complex roles are scoped separately. Full hardening, code audit and restore testing are excluded.
Final scope, scheduling, access, availability and commercial terms require written confirmation. Onsite visits, travel, additional assets and production changes are separate.
Confirm the business question, authorised assets and working access.
Complete the agreed checks and record coverage limitations.
Organise findings by practical risk and remediation sequence.
Verify agreed fixes once within 30 days and the original scope.
The engagement is complete when you understand what was covered, what matters first and what sits outside the agreed scope.
Reachable systems, checks completed and any access limitations.
Business context for decisions plus technical detail for remediation.
A handover and one recheck within the original agreed boundary.
Yes. The packages assume working, authorised remote access and the permissions needed for the agreed checks. Providing new connectivity, accounts or access infrastructure is separate work.
Only when the agreed assessment method requires it and you have authorised it. The scan position, credentials, temporary tools and removal steps are confirmed before work begins; nothing is installed without approval.
Yes, where the operating system and server role are supported. The focused server review covers one supported Windows or Linux server, subject to suitable access and a confirmed scope.
The Business Network Vulnerability Assessment covers one business site or network and up to 25 reachable assets. The Server Security Review covers one supported server. Additional sites, assets or complex roles are scoped separately.
Security checks generate network traffic and can affect fragile systems. Compuloop agrees an appropriate window, scan intensity and exclusions before starting, but cannot promise zero impact on every device.
Offline or unreachable devices cannot be assessed. They are recorded as a coverage limitation, and any return visit or expanded scope is agreed separately.
Findings are reviewed before handover so likely noise can be separated from actionable issues. Validation remains within the authorised assessment boundary and does not include exploitation unless separately agreed.
No. Production changes, patching and hardening are separately scoped. One recheck within 30 days is included after agreed fixes are made and remains within the original assessment boundary.
The report records reachable systems, coverage limitations and reviewed findings, then organises the work by practical risk and remediation sequence. The handover explains what matters first and what requires further investigation.
One recheck within 30 days is included for agreed fixes in the original scope. A new assessment is useful after material infrastructure changes or on a risk-based schedule; recurring work is quoted separately.
Independent guidance: ASD small business cyber security handbook. It complements the service scope; it does not certify this service.